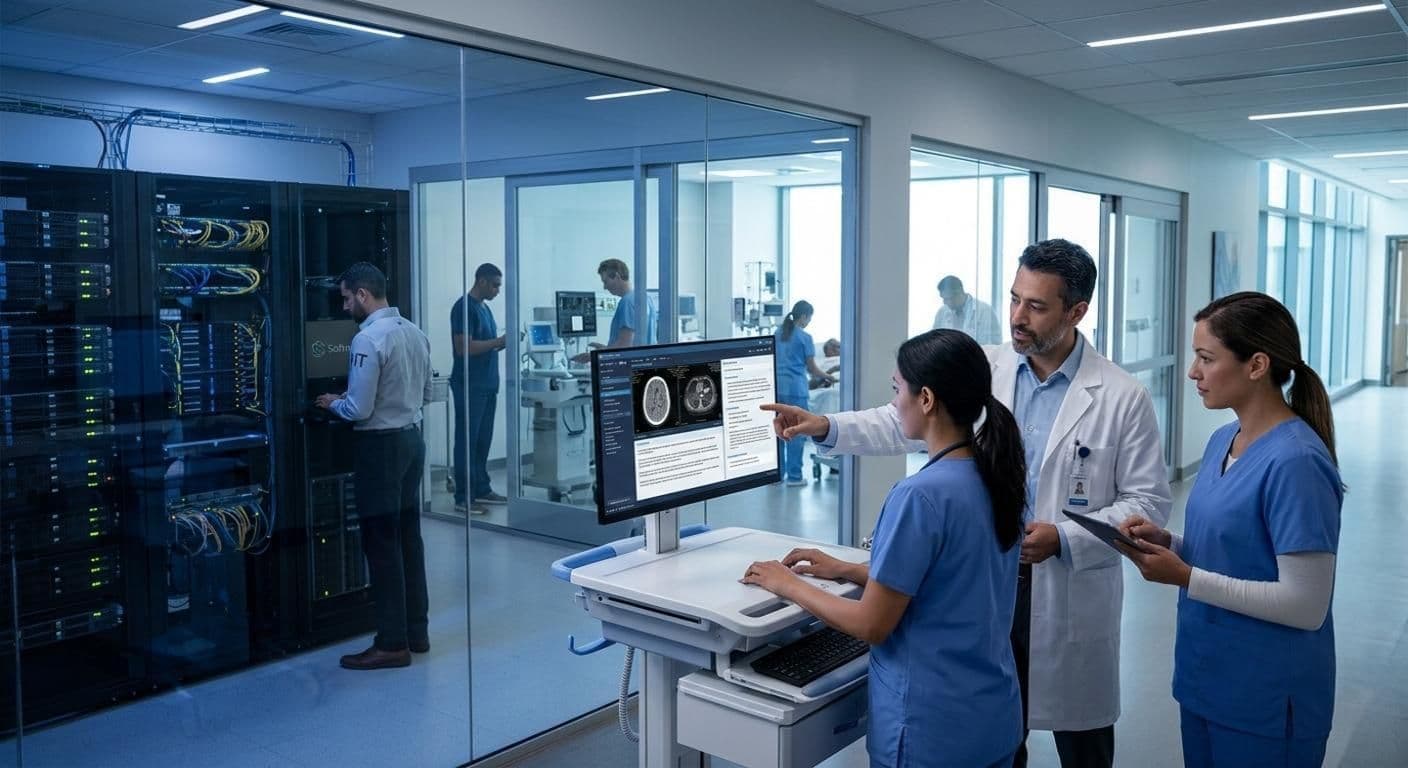
HIPAA in the Age of AI: What Changes When You Add LLMs to Your Clinical Workflow?
Learn how U.S. healthcare organizations can integrate LLMs into clinical workflows while managing PHI, vendors, security, access, and HIPAA requirements.
 Lokesh ML
HIPAA and LLMs in Clinical Workflows: What Healthcare CXOs Need to Know
Large Language Models (LLMs) are becoming increasingly useful across healthcare. They can assist with clinical documentation, summarize information, support patient communication, help staff process information, and improve operational workflows.
But introducing an LLM into a healthcare workflow can also introduce new data flows, vendors, access points, security considerations, and governance responsibilities.
For a U.S. healthcare organization, the question is :
What information will the LLM receive? Where will that information go? Who can access it? What will the provider do with it? And what controls will remain in place after deployment?
When protected health information (PHI) is involved, these questions become particularly important.
HIPAA's Security Rule requires regulated entities to assess risks and vulnerabilities to electronic protected health information (ePHI) and implement appropriate safeguards. HHS describes risk analysis as a foundational and ongoing part of the Security Rule compliance process.
This is where Healthcare Software Development Services can play an important role: designing the AI-enabled workflow so that security, privacy, access control, auditability, and governance are considered as part of the architecture, not added after the AI solution is built.
What Changes When an LLM Enters a Clinical Workflow?
An existing workflow might look relatively straightforward:
EHR → Healthcare Application → Clinician
Introducing an LLM can create additional components:
EHR → Application → AI Gateway → LLM → Application → Clinician
Depending on the architecture, there may also be cloud infrastructure, APIs, logging systems, monitoring tools, third-party services, and other integrations.
This does not mean that every LLM implementation automatically creates the same HIPAA obligations.
Start With the Data Flow, Not the AI Model
One of the first questions a healthcare CIO, CTO, or CISO should ask is:
What data actually leaves the healthcare organization's controlled environment?
Before integrating an LLM, map the complete flow of information.
For example: Patient record → Clinical application → AI integration layer → LLM provider → Generated response → Clinical application → Clinician
For each step, determine:
What data is being transmitted?
Does it contain PHI?
Who receives it?
Where is it processed?
Is it stored?
How long is it retained?
Who can access it?
Is it used for any other purpose?
How is it protected in transit and at rest?
This data-flow exercise should be part of the organization's broader HIPAA risk analysis. HHS states that the Security Rule's risk analysis encompasses ePHI created, received, maintained, or transmitted by the organization.
Understand the Role of the AI Vendor
If a third party is acting as a business associate and handling PHI on behalf of a covered entity, the relationship generally requires an appropriate Business Associate Agreement (BAA) and contractual safeguards.
HHS specifies that a business associate agreement must establish permitted uses and disclosures of PHI and require appropriate safeguards. Business associates can also have direct obligations under HIPAA.
For an LLM or AI platform, healthcare organizations should therefore establish:
- Whether PHI will be processed
- The provider's role in the workflow
- Whether a BAA is applicable
- What data the provider receives
- How the data is protected
- Whether data is retained
- Whether data is used for other purposes
- What happens when the relationship ends
- How security incidents are handled
- What subcontractors may have access to the data
A BAA, however, should not be treated as the entire compliance strategy. It is one component of a broader risk-management and security approach.
Minimize the PHI Sent to the LLM
HIPAA's Privacy Rule generally requires covered entities to make reasonable efforts to limit uses, disclosures, and requests for PHI to the minimum necessary to accomplish the intended purpose, subject to important exceptions such as treatment disclosures.
For an AI workflow, this can translate into architectural decisions such as:
- Sending only relevant clinical information
- Removing unnecessary identifiers where appropriate
- Limiting the context provided to the model
- Restricting access based on user roles
- Separating sensitive data from general application data
- Applying data-retention policies appropriate to the use case
This is where the difference between adding an LLM to an application and engineering an AI-enabled healthcare workflow becomes significant.
Secure the AI Integration Layer
The AI model is only one component of the system. The integration layer connecting the healthcare environment to the AI service can become an important security boundary.
A healthcare AI architecture may require controls around:
Access Management - Only authorized users and systems should be able to invoke the AI workflow or access its outputs.
Authentication - Systems should verify the identity of users and connected services.
Encryption - Data should be appropriately protected while being transmitted and stored.
API Security - AI integrations should be designed with appropriate authentication, authorization, validation, rate limiting, and monitoring controls.
Audit Logging - Organizations should be able to understand who accessed the system, what actions occurred, and when.
HIPAA's Security Rule includes requirements addressing access control, audit controls, authentication, and transmission security for ePHI.
The architecture should therefore treat the LLM integration as part of the healthcare application's security boundary, not as an isolated AI feature.
Don't Treat HIPAA as a Pre-Go-Live Checklist
For AI-enabled healthcare workflows, governance needs to continue after deployment. HHS describes HIPAA risk analysis as an ongoing process and notes that organizations should update their analysis and security measures as needed.
Post-deployment monitoring should consider:
- Access activity
- Security events
- AI usage
- Data flows
- Vendor changes
- Model or system changes
- User-reported issues
- Clinical workflow impact
- Performance and accuracy
- Compliance risks
The objective is not to monitor everything equally.
It is to establish monitoring that is proportionate to the workflow's risk and intended use.
Cloud and AI Infrastructure Need the Same Attention
Many LLM implementations depend on cloud infrastructure. That does not automatically make the architecture non-compliant.
HHS states that a HIPAA covered entity or business associate may use cloud services to store or process ePHI when the applicable HIPAA requirements are met, including an appropriate BAA with the cloud service provider when it is acting as a business associate. The organization must also understand the cloud environment as part of its risk analysis.
What Healthcare CXOs Should Ask Before Approving an LLM
Before an LLM becomes part of a clinical workflow, leadership should be able to answer:
Data
- What information will the model receive?
- Does it contain PHI?
- Is the data flow documented?
Vendor
- Who is processing the data?
- What is the vendor's role?
- Is a BAA required?
- What happens to the data after processing?
Security
- How is the integration protected?
- Who can access it?
- What is logged?
- How are security incidents detected and handled?
Clinical
- Is the AI output advisory or decision-influencing?
- What level of human review is required?
- How are errors identified and escalated?
Governance
- Who owns the AI system?
- Who approves changes?
- Who monitors performance?
- When should the system be reassessed or retired?
Business
- What problem is the AI solving?
- What outcome is expected?
- How will leadership know whether it is delivering value?
If these questions cannot be answered clearly, the organization may not yet be ready to put the AI workflow into production.
How Softnotions Can Help
Adding an LLM to an existing healthcare application can look simple from the outside.
The complexity lies in everything around it including Data, Integration, Security, Workflow, AI, Governance & Monitoring
Important Note - HIPAA requirements depend on the specific organization, workflow, data involved, vendor relationships, and intended use.
This is where Softnotions' Healthcare Software Development Services can help.
We can work with healthcare organizations to design and engineer AI-enabled workflows with considerations for:
- Secure healthcare application architecture
- PHI-aware data flows
- AI and LLM integration
- Healthcare data engineering
- API and system integration
- Access control and authentication
- Auditability and monitoring
- Cloud architecture
- Human-in-the-loop workflows
- AI governance and lifecycle management
- Application modernization
The objective is not simply to connect an LLM to a healthcare application. It is to engineer the surrounding technology and workflow so that AI can be introduced responsibly, securely, and at scale.
Let's work together to solve your business challenge
Connect with us and let's start the journey toward your next breakthrough.
Schedule a Discovery Call
Lokesh ML
CTO
With over 20 years in software engineering and technology leadership, I help healthcare organisations design, build, and scale secure AI-driven digital solutions that solve real clinical and operational challenges.
As CTO at Softnotions, I lead a team of engineers delivering Healthcare Data & AI platforms, custom EHR integrations, and intelligent automation systems. Our work spans clinical decision support, and healthcare data interoperability built with a strong focus on security, compliance, and scalability.